An Override Policy is a high-priority access rule that guarantees specific traffic is permitted regardless of other matching policies. It ensures specific traffic is always permitted — even when deny policies exist — while maintaining structured policy enforcement across inbound, outbound, and application policies.
The override functionality can be configured only for ALLOW policies and is defined as ALLOW (!) under Firewall Configuration.
The feature is available for new customers as well as existing customers who already have firewall policies configured.
Policy override applies to all three firewall policy types:
- Inbound policies (L4)
- Outbound policies (L4)
- Application policies (L7)
Policy Evaluation Order
When a user applies an override policy, firewall rule evaluation follows the order:
- ALLOW (!) — an Override Allow policy
- DENY — a Block policy
- ALLOW — a Standard Allow policy
Key Behaviour:
- If traffic matches an ALLOW (!) policy, the policy evaluation stops immediately.
- The traffic is permitted according to the override ALLOW (!) policy definition.
- Any matching DENY policies are ignored.
Example – Adding override application policy to allow LinkedIn Only
- Step 1: Block Social Networks — Under Application Policies (L7), a DENY policy is configured to block the social networks such as Facebook, Instagram and LinkedIn.
- Step 2: Add Override Allow policy for LinkedIn — Create an override ALLOW (!) policy specifically for LinkedIn.
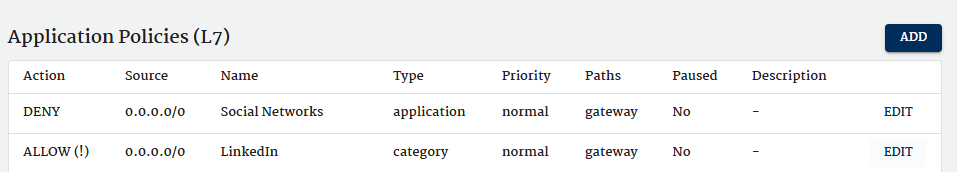
The application name must be entered exactly as defined in the system.
Users can verify the correct application name using the Application Lookup tab before creating the override policy to ensure the rule applies correctly.
Results:
- All Social Network applications (Facebook, Instagram, etc.) remain blocked.
- LinkedIn is allowed due to the Override ALLOW (!).
- The override policy takes the highest precedence, bypassing the broader DENY rule.